









Proof, not logs.
You only pay for people who run or approve agents that month. Auditors are free. Beta pricing, may change.
 Euthyne
Any agent, any workflow. Every action becomes a signed, tamper-evident receipt, anchored on-chain and verifiable by anyone. Your prompts and outputs stay with you.
 EuthyneFileEditView
Through each agent's native hooks. Euthyne records Claude Code, Codex, GitHub Copilot CLI, Cursor, Gemini CLI, Antigravity CLI, Devin Desktop, OpenCode, Grok Build and Hermes Agent today.
Proof for auditors, clients and insurers.
When an agent misbehaves, Euthyne shows which agent did it, for whom, with what access, and proves the record was never edited.
Today · 1,284 actions sealed
You only pay for people who run or approve agents that month. Auditors are free. Beta pricing, may change.
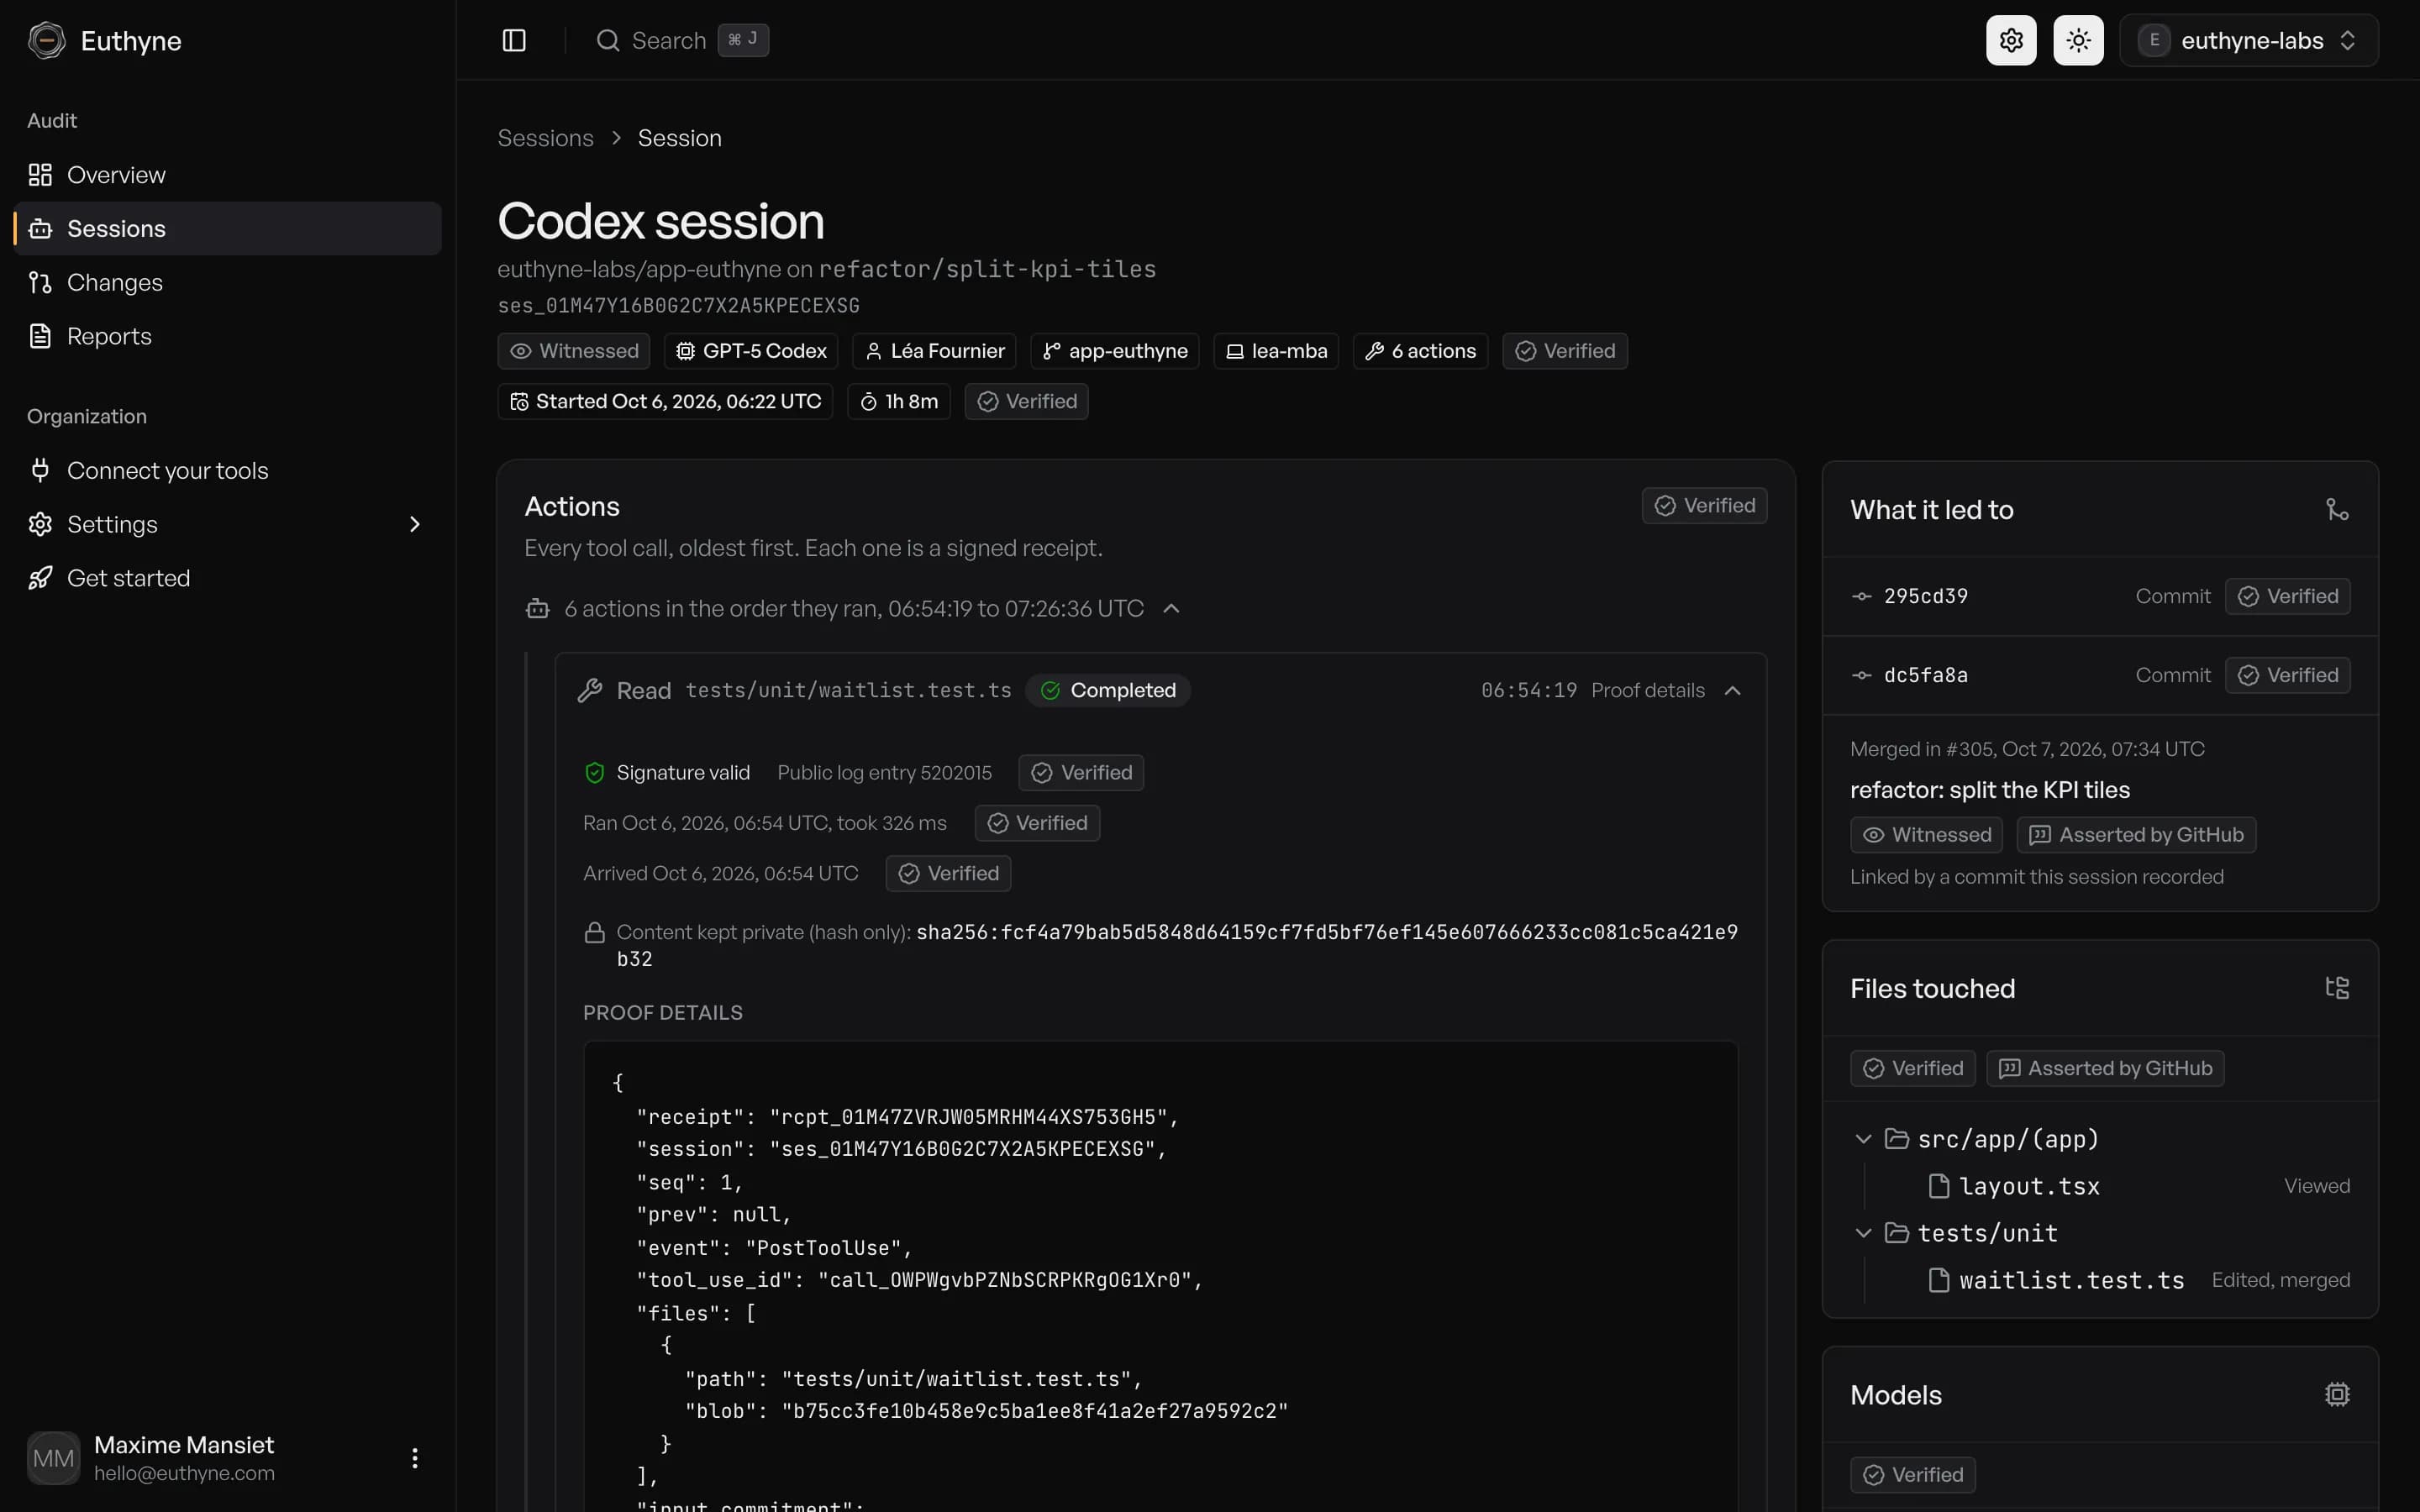
Euthyne is a forensic audit layer for AI agents. Every action an agent takes becomes a signed, tamper-evident receipt that records which agent acted, on whose behalf, with which model and with what access. Receipts are anchored on-chain and anyone can verify them.
Euthyne plugs into the tools your agents already run in, through their native hooks and your git host. Nothing sits between your agents and their models, and your agent logic does not change.
Euthyne records Claude Code, Codex, GitHub Copilot CLI, Cursor, Gemini CLI, Antigravity CLI, Devin Desktop, OpenCode, Grok Build and Hermes Agent today. It works with any model, and receipts look the same whichever agent or model produced the action.
No. Prompts, outputs, commands and file contents are hashed with salts that stay with you, before anything leaves your machine. Euthyne sees who acted, with which agent and model, and when, never what was said.
Not for the record itself. Each receipt is signed at the source and added to an append-only log whose checkpoints are anchored on-chain. Alter or delete one and verification fails, for anyone who runs euthyne verify, with no account needed. Agent and organization identities are W3C Verifiable Credentials.
Free for individuals and open source. Team is €29 per month with 5 active members included, Company is €25 per active member per month. You only pay for people who run or approve agents that month, and auditors are free.
Euthyne is built for SOC 2 change management, ISO 42001 and EU AI Act record-keeping (Art. 12). Every receipt ties an action to an agent identity and the human behind it, in a history no one can quietly rewrite. Binding each change to its approval is coming soon.
Something missing? Write to hello@euthyne.com.
Euthyne is in public beta. Leave your email and we’ll reach out.